



Deploy wg-easy in one click
Your own WireGuard VPN, ready in minutes
WireGuard Easy is the most popular open-source web interface for running a self-hosted WireGuard VPN server – manage devices from the browser instead of editing configs over SSH.
-

 Add devices with QR codes
-

 One-time config links
-

 Client expiration dates
-

 TOTP two-factor login
-

 Real-time traffic statistics
-

 IPv6 and IPv4 support

 Installs with
your VPS

 Full root
access

 Live in
~5 minutes

 Instant
dashboard access
Key features
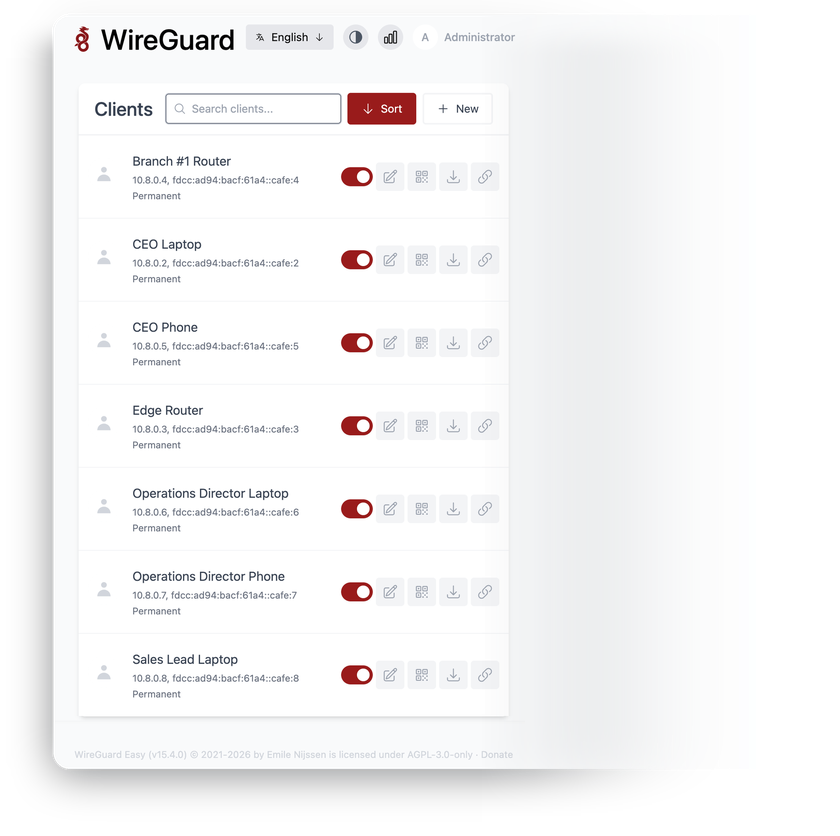
List, create, edit, enable, disable, and delete WireGuard clients from the browser – no manual config editing on the server.
Allowed IP restrictions and firewall filtering are enforced on the server side, limiting each peer to the networks it actually needs.
See which clients are online right now, with Tx/Rx charts for every connected peer.
Hand a new user their tunnel through an expiring single-use link instead of sending config files over chat or email.
Protect the dashboard with time-based codes from any authenticator app – enabled per user from the account page.
Phones, laptops, and routers connect with the stock WireGuard apps for iOS, Android, Windows, macOS, and Linux – no proprietary client software on any platform.
System requirements
View All VPS Options
Get started in 4 easy steps
-
1
Select a VPS plan
Choose the virtual server resources and performance tiers that fit your project requirements.
-
2
Pick your application
Browse our marketplace during VPS setup and select the self-hosted software you want to deploy.
-
3
Complete the payment
Pay the standard virtual server invoice – the 1-click deployment tool itself is fully complimentary.
-
4
Complete and access
Your server provisions and automatically installs the software. Once the setup process finishes, your new environment is fully ready for you to connect and use.
Deployment details
Application
wg-easy 15 – latest 15.x release, official image
- Deployed with Docker Compose from the vendor's registry
- Admin account created automatically – no setup wizard


VPN and firewall
WireGuard data plane on UDP port 51820
- Default-drop nftables firewall – only SSH, web, VPN, and DHCPv6 client ports open
- Tunnel IPv6 enables automatically when the VPS has global IPv6


Web access and SSL
Nginx serving the admin panel over HTTPS
- Web UI reachable through nginx on 443
- Self-signed certificate by default – setup-ssl issues a free Let's Encrypt certificate


Software licensing
AGPL-3.0-only – open-source, no license fees
- No device limits, feature gates, or paid tiers
- Full AGPL-3.0 license text
Why deploy on INTROSERV
-


NVMe storage
Every VPS runs on NVMe drives – fast I/O for databases, metrics, and busy workloads.
-


Locations in Europe and the US
Deploy close to your infrastructure and users – lower latency, regional compliance.
-


Unmetered traffic
No bandwidth caps and no overage bills – your monthly price stays predictable.
-


IPv4 and IPv6 included
A dedicated IPv4 address plus native IPv6 with every server.
-


24/7 human support
Engineers on duty around the clock – real answers, not ticket bots.
-


Scale anytime
Upgrade CPU, RAM, or storage as your workload grows – without migrating.
Terms and support boundaries
Infrastructure and support limits
Our company provides the Virtual Private Server infrastructure and the automation script for initial deployment. While we guarantee the availability and performance of your hardware and network, our technical support exclusively covers infrastructure-related issues – such as server connectivity, hardware stability, and billing. Assistance with application-specific configuration, software bugs, or user management is the responsibility of the server administrator or software maintainers.
Software licensing and compliance
All marketplace tools deploy standard versions of third-party software products and are provided "as-is" with no modifications to their original code. While the core of many available applications is open-source, using proprietary features or advanced enterprise tiers in production environments may be subject to the vendor's specific licensing terms. Users must manage and acquire any required commercial subscriptions directly from the software developers.
FAQ
-
Do I need a license to run wg-easy?
No. Since version 15, wg-easy is released under the GNU Affero General Public License v3 (AGPL-3.0-only) – fully open-source, with no paid tiers or device limits. You only pay the standard virtual server invoice.
-
How do I log in after deployment?
Once the server is provisioned, you'll find the web interface URL, the admin login, and a securely generated password in your INTROSERV panel. The same details are shown at SSH login and stored in /root/credentials.txt, readable by root only. After the first sign-in, we recommend enabling two-factor authentication from the account page.
-
How do I get a valid SSL certificate?
The admin panel ships with a self-signed certificate enabled by default. To issue a free Let's Encrypt certificate for your own domain or the server's FQDN, connect over SSH and run the setup-ssl script – one command, no manual configuration. After switching to a domain, also update the Host field in the wg-easy admin panel, so that new client configs use the domain as the WireGuard endpoint.
-
How do I connect my first device?
Create a client in the web interface, then scan the QR code with the official WireGuard app on your phone – or download the config file for desktops and routers. The tunnel comes up immediately; no changes are needed on the server side.
-
Can I migrate an existing wg-easy installation?
Yes. The project publishes an official migration guide for moving from older wg-easy versions, and version 15 stores everything – clients, keys, settings – in a single data volume. Back up that volume on your current server, restore it into the volume on the new one, and your peers reconnect to the new endpoint.
-
How are updates handled?
The deployment tracks the official 15.x release branch. Pulling a new version is two documented commands on the server – nothing updates behind your back, and the exact update line is stored in /root/credentials.txt.
-
Is the admin panel exposed to the internet?
The panel itself listens on localhost only and is reachable exclusively through nginx over HTTPS. The host firewall defaults to dropping everything except SSH, web ports, and the WireGuard UDP port – there is no direct path to the application or the database.
-
What if I outgrow my configuration?
WireGuard throughput is CPU-bound, so when many devices push traffic at once, upgrade the vCore count of your VPS – no reinstallation needed. Disk and RAM rarely become the bottleneck: the entire wg-easy state is a small database, not a growing data store.




